Cytex · AI & agent security

Your AI agents take action.
Keep control.

Test AI behavior, control agent access to tools and sensitive data, investigate activity, and track spend alongside enterprise cyber risk.

Works with your existing cloud, security, and AI stack

The Cytex platform

See how your
risks connect.

Cytex connects cybersecurity, AI and agent security, data security, and continuous compliance in one platform.

Bring cloud posture, sensitive-data findings, endpoint signals, and risk workflows together. Extend that context into AI models, agent sessions, and the data their tools can reach.

See how the connections work

Meet AICenturion

AICenturion
Security for models and agents.

Discover AI in network traffic, code, scans, and logs. Test model behavior, apply runtime guardrails, and investigate agent access with MCP Guardian.

Evaluation & red teaming

Test models
before release.

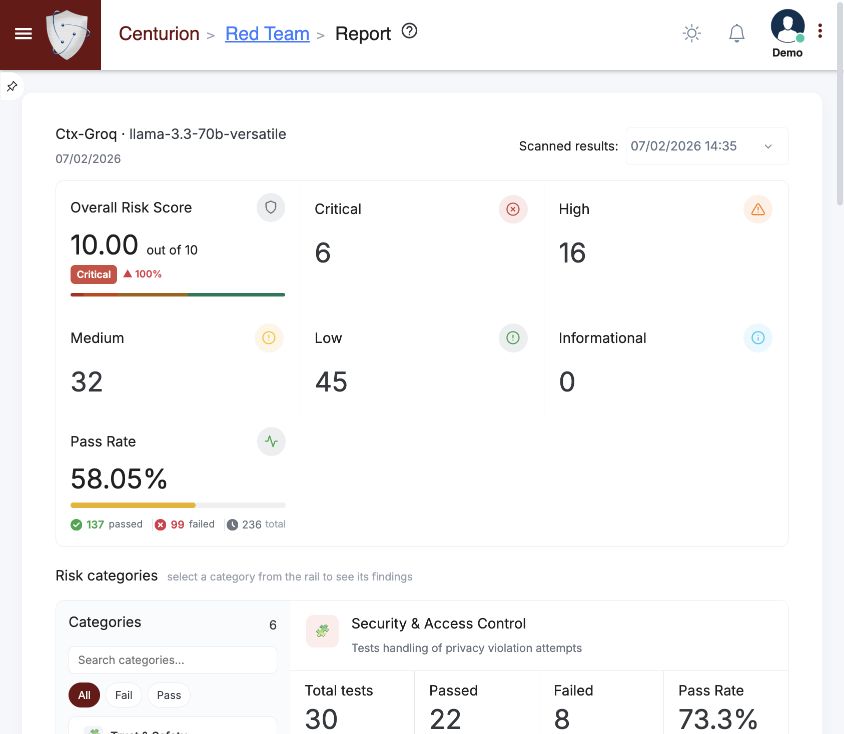
Examine how models handle privacy, security, bias, and harmful content. Move from a pass rate to the specific tests and findings behind it.

  • Compare pass, fail, and error results across evaluations.
  • Investigate red-team findings by severity and attack method.
  • Connect test evidence to NIST AI RMF, ISO/IEC 42001, and other framework controls.
See an evaluation walkthrough
Cytex Red Team report showing risk severity, pass and fail totals, and Security & Access Control findings using sample data.
Cytex Red Team · Demo dataView full screenshot

Actual screens from the Cytex demo. Figures are sample data, not benchmarks or customer results. Framework mappings support assessment; they do not certify compliance.

Explore the Cytex platform

Security across
your enterprise.

Connect cloud, data, vendor, and software risks with the controls and evidence used to manage them.

Cloud security

Find exposure across your cloud.

Monitor cloud posture and SaaS configurations. Connect vulnerabilities, identity access, and asset context to focus remediation.

CSPMCloud app security
Explore cloud security
Data security

See who can reach sensitive data.

Discover sensitive information and understand its exposure. Connect permissions, identities, and AI activity to data risk.

DSPMIdentity & access context
Explore data security
Audify · Compliance Ops

Keep audit evidence current.

Organize audits, documents, and checklists alongside control evidence. Track gaps and remediation, and reuse relevant evidence across overlapping framework requirements.

Continuous complianceControl mapping
Explore compliance automation
Third-party risk

Assess vendor exposure.

Assess vendors and monitor changes in their security posture. Put third-party risk in the context of business access and dependencies.

TPRMContinuous monitoring
Explore vendor risk
Software & AI supply chain

Inspect software and AI dependencies.

Bring component inventories, dependency risk, and security checks into the development lifecycle with SBOM, AIBOM, and DevSecOps capabilities.

SBOM / AIBOMDevSecOps
Explore software assurance
People & resilience

Help people recognize threats.

Build security awareness with training and phishing simulations. Help teams recognize threats and make better decisions in their daily work.

Security awarenessPhishing simulations
Explore security awareness

The Cytex Risk Graph

Trace a finding
to business impact.

A vulnerable workload is one finding. Connect it to a privileged identity, sensitive data, and an AI agent, and the business impact becomes clearer.

Cytex connects these relationships so your team can see the path, understand the exposure, and prioritize the control that breaks it.

Explore connected risk in a demo

Illustrative risk path

Entry point

Exposed cloud workload

An exploitable vulnerability opens a path.

Access

Privileged service identity

Its permissions extend the potential reach.

AI activity

Agent uses the same trust path

Autonomous actions inherit the exposure.

Business impact

Sensitive customer data

Prioritize the controls that protect it.

Use the risk path to choose where to intervene.

Built around your responsibilities

What does your
team need to solve?

Explore the workflows relevant to your role.

For security leaders

Investigate AI risk
alongside cyber risk.

Bring shadow AI, guardrail events, sensitive-data exposure, and enterprise risk into one conversation. Investigate the activity behind an alert and the assets it could affect.

Book a security-focused demo
  • Prioritize material exposure

    Connect correlated findings in the Risk Graph with AI discovery and security events.

  • Govern autonomous access

    Inspect prompt and response guardrails, redaction, and MCP session outcomes.

  • Support board accountability

    Connect operational risk, controls, and remediation evidence.

Works with your existing tech stack

Your stack.
Connected to Cytex.

Cytex and AICenturion integrate with the cloud platforms, security tools, business applications, and AI services your teams already use.

Connect enterprise signals with model and agent activity, so security reviews include the systems and data those agents can reach.

See how Cytex fits your stack

Cloud & infrastructure

Connect cloud accounts, storage, and infrastructure signals.

AWS · Microsoft Azure · Google Cloud Platform · Amazon S3 · Amazon EKS

Identity & access

Bring identity and access context into your security review.

Microsoft Entra ID · Okta · Auth0 · Duo · OneLogin

Security operations

Connect the security tools your team already uses.

CrowdStrike · SentinelOne · AWS GuardDuty · Carbon Black · Snyk

Workplace & development

Include the applications where your people and code work.

Microsoft 365 · Google Workspace · GitHub · GitLab · Jira · Salesforce · Slack · ServiceNow

AI providers & observability

Bring model providers and AI engineering tools into scope.

Anthropic · OpenAI · Gemini · AWS Bedrock · Groq · Ollama · Microsoft Copilot · Langfuse · MLflow

MCP tools & data

Review agent connections to tools, databases, and services.

PostgreSQL · Context7 · Cloudflare · Firecrawl · Playwright

Selected entries from the Cytex integration catalog. Connection methods, permissions, and availability vary by connector; some MCP integrations are request-based.

Bring your stack to a demo

Resources

Explore the thinking
behind the controls.

Product information and cybersecurity commentary from Cytex.

Discuss your use case with Cytex

Frequently asked questions

Evaluating Cytex

Discuss your use case
What is MCP Guardian?

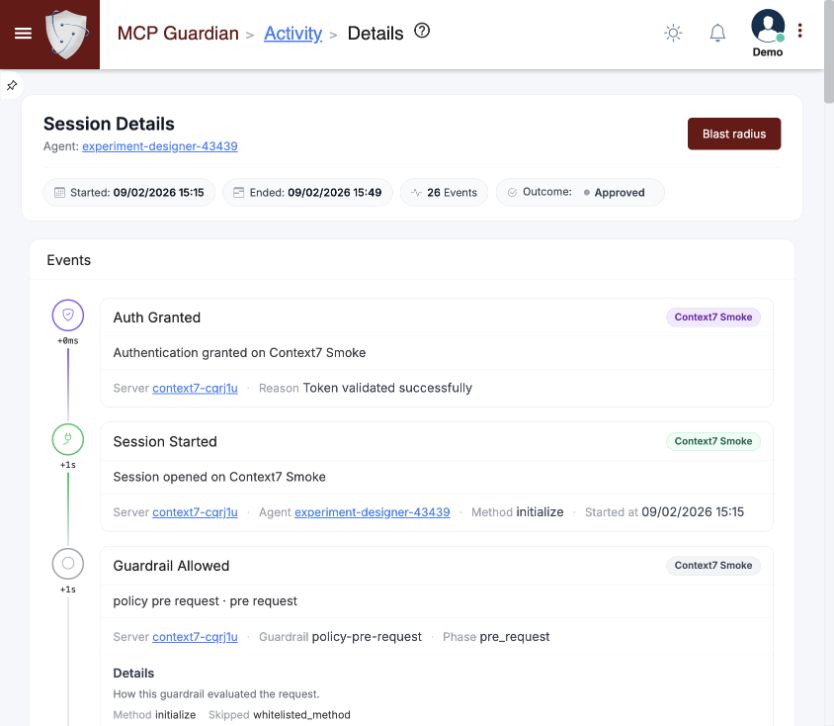
MCP Guardian is part of Cytex's AI and agent security capabilities. MCP stands for Model Context Protocol, which connects AI applications with tools and data sources. MCP Guardian records agent sessions, authentication, guardrail evaluations, policy decisions, and outcomes so teams can investigate tool activity and affected data.

What does Cytex do?

Cytex connects cybersecurity, AI and agent security, data security, and continuous compliance. It helps teams understand how enterprise risks relate, prioritize remediation, govern AI activity, and maintain evidence of operating controls.

How is AICenturion related to Cytex?

AICenturion is Cytex's security offering for AI models and agents. It brings together AI discovery, model evaluation, red teaming, runtime guardrails, and spend management. MCP Guardian adds visibility into agent sessions, tool interactions, policy decisions, and data dependencies.

Does AICenturion enforce policies or only monitor AI?

AICenturion supports runtime policy enforcement, including controls over prompts, responses, sensitive data, and agent interactions with tools and MCP servers. The connected systems and deployment configuration determine the coverage to evaluate in your demo.

Does Cytex work with an existing security stack?

Yes. Cytex and AICenturion integrate with existing cloud, identity, security, business, and AI systems. The catalog includes AWS, Microsoft Azure, Google Cloud, Microsoft 365, GitHub, Salesforce, Anthropic, OpenAI, and other providers and tools. Connection methods, permissions, and availability vary by connector; a demo can confirm the coverage your environment needs.

How does Cytex support compliance and AI governance?

Cytex automates evidence collection, tracks control gaps, and supports control mapping and remediation. AICenturion adds AI inventories, evaluations, policy decisions, and activity records. Framework support helps your governance program; it is not a certification or a guarantee of compliance.

What will a Cytex demo cover?

A tailored demo can follow your priorities: discover AI use, review a red-team report, investigate an agent session and its data impact, define an AI spending profile, or trace evidence to framework controls. Bring a use case to discuss integration and deployment scope.

What can I investigate with MCP Guardian?

MCP Guardian provides session timelines for agent and tool activity, including authentication, guardrail evaluations, policy application, redaction, errors, and outcomes. Session blast-radius views and data lineage help teams investigate affected assets and downstream dependencies.

Can Cytex help manage AI spending?

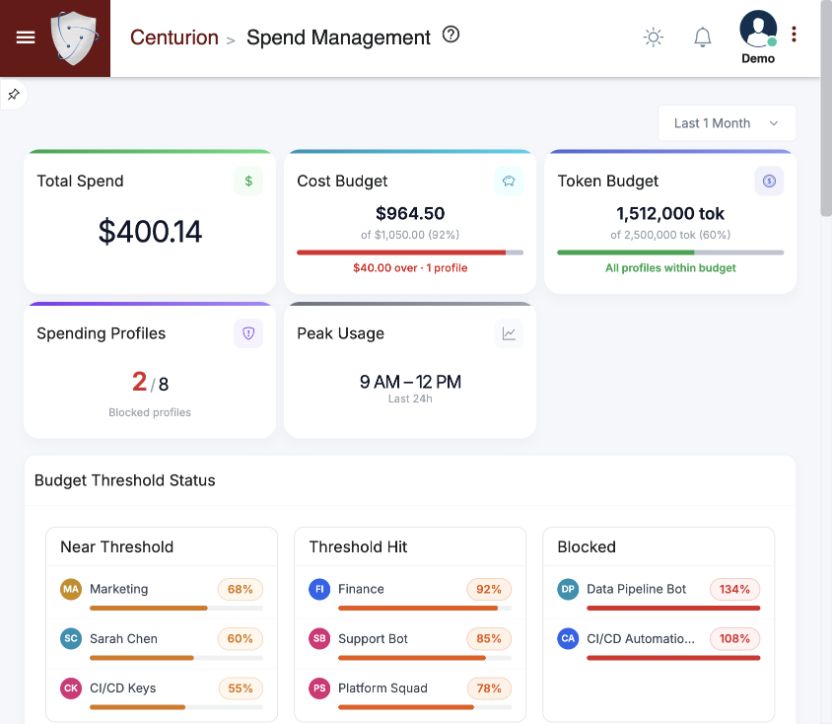
Spend Management provides token and dollar budget profiles for users, groups, departments, and non-human API-key identities. Teams can review weekly or monthly budgets, usage, threshold status, and spending by model and identity.
See Cytex in action

See Cytex with
your use case.

Choose a time for a demo. Bring an AI workflow, a risk question, or an audit requirement you want to explore.

Your demo can cover

  • Shadow AI, security events, and connected risk
  • MCP guardrails, session evidence, and affected data
  • Controls, remediation, and board-ready evidence
Open booking calendar

Choose a time below, or open the calendar in a new tab.